DNS monitor
Matches LLM APIs and agent infrastructure using exact domains and provider-aware suffix rules.
Open-source AI infrastructure discovery
AgentSniff combines active probing, passive observation, protocol detection, and signal fusion to surface AI-agent infrastructure—with evidence you can inspect.
curl -fsSL https://agentsniff.org/install.sh | bash
Linux & macOS · requires Cosign to verify release provenance. Windows binaries are available on GitHub Releases.
Correlated evidence03 signals
Operator view
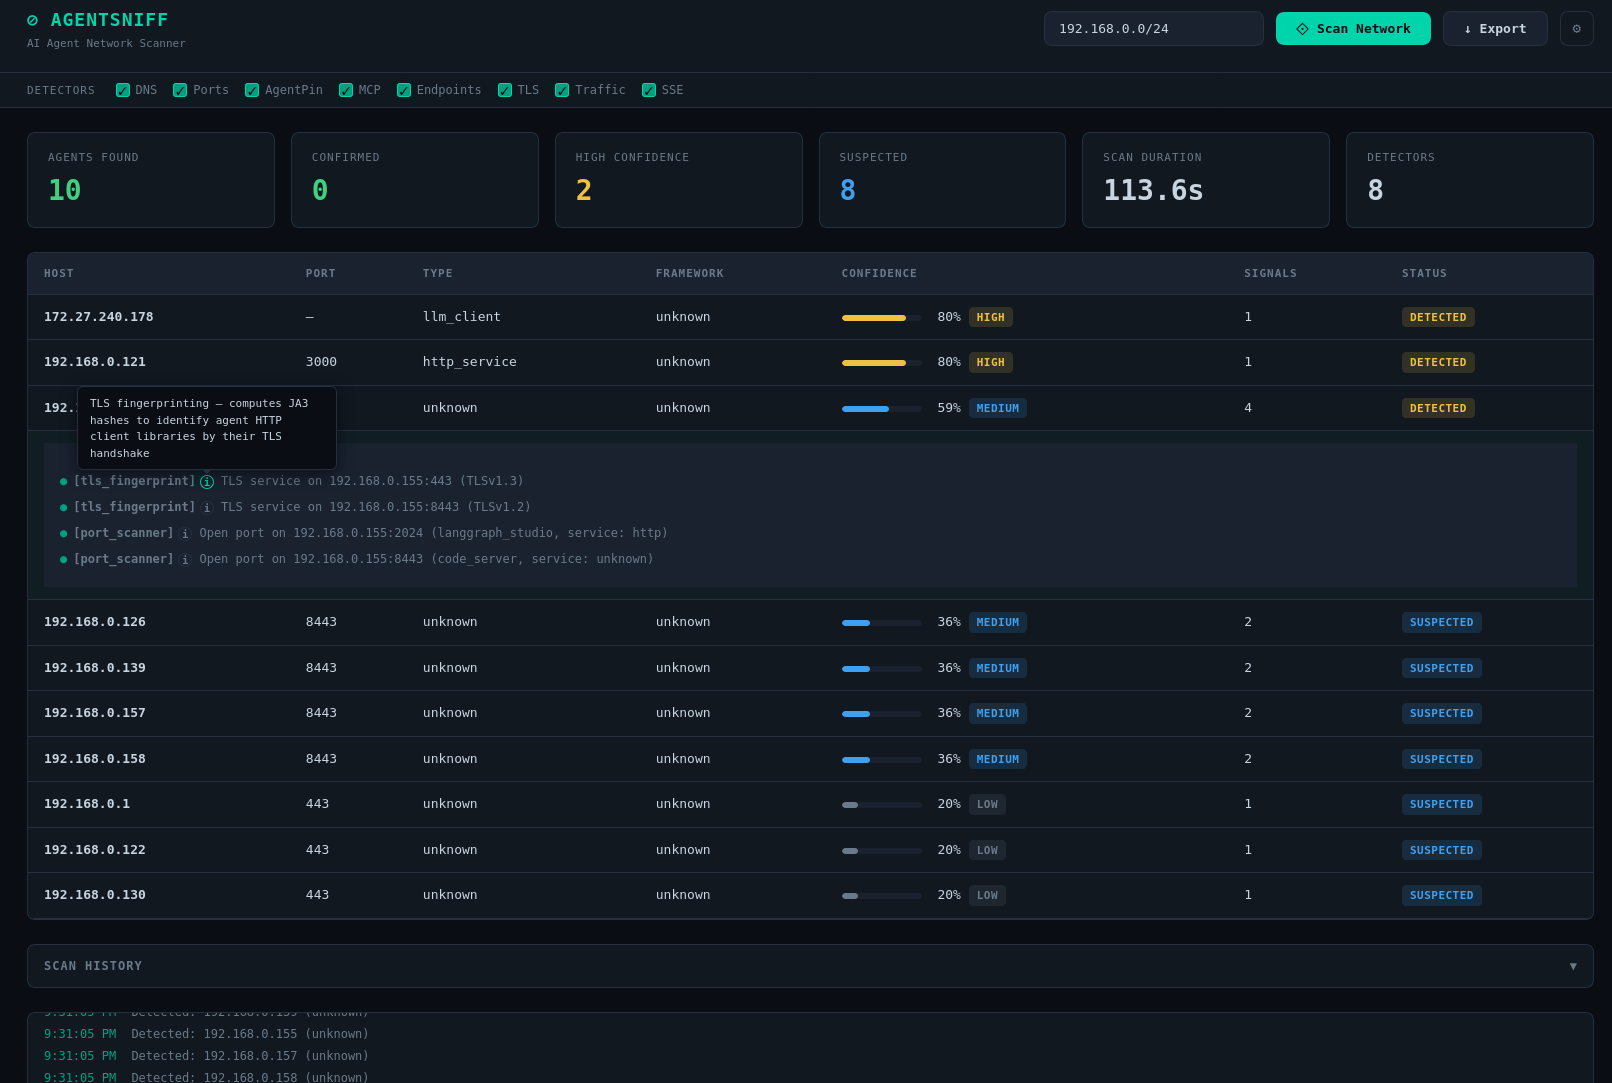
Launch and stop scans, choose detectors, follow live results, inspect evidence, and return to stored scan history from one local dashboard.
Detection model
Detectors run concurrently and correlate evidence by source host with noisy-OR scoring. Weak indicators stay weak; corroboration raises confidence.
Matches LLM APIs and agent infrastructure using exact domains and provider-aware suffix rules.
Finds MCP, inference, vector, agent-platform, and IDE-agent services without treating an open port as identity.
Discovers AgentPin documents as self-asserted evidence, without overstating unsigned metadata as verified identity.
Validates Agent Cards and can verify ES256 signatures against operator-configured trusted keys.
Negotiates current and legacy MCP protocol versions, then enumerates exposed tools, resources, and prompts.
Checks framework routes, response headers, OpenAPI documents, metadata standards, and client signatures.
Uses JA3 and JA4 client-library hints as supporting evidence, not standalone agent identity.
Looks for burst behavior, observe-reason-act timing, API diversity, and known LLM connections.
Surfaces long-lived event-stream traffic associated with streamed model responses and agent activity.
Secure by default
AgentSniff separates discovery evidence from verified identity, constrains network-facing behavior, and keeps optional privileged capture explicit.
release / provenance
The one-line installer fails closed unless Cosign verifies the archive against the expected GitHub Actions release identity.
signal / confidence
Low-confidence catalog matches remain hints. Protocol responses and locally trusted signatures can produce stronger conclusions.
Quick start
Install from crates.io, scan a network you are authorized to test, or start the loopback dashboard.
Full installation guide# Install the Rust CLI $ cargo install agentsniff --locked # Discover agent infrastructure $ agentsniff scan 192.168.1.0/24 # Scan selected detectors $ agentsniff scan 10.0.0.0/24 \ --detectors mcp_detector,a2a_detector # Start the local dashboard $ agentsniff serve --port 9090